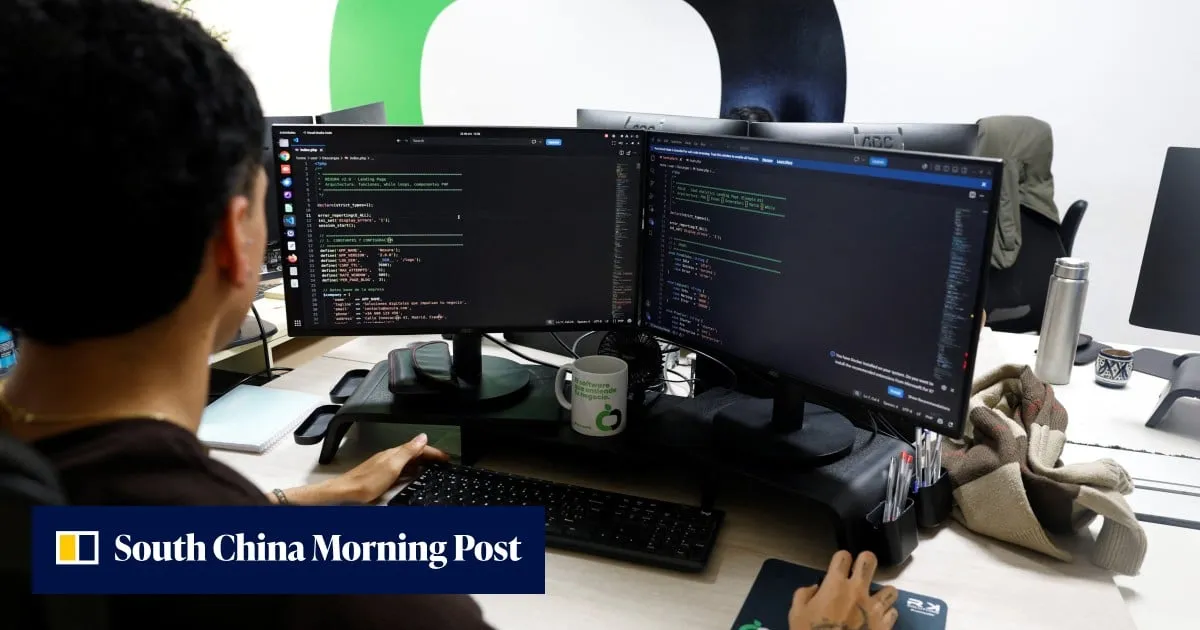
Organisations in Singapore have been urged to immediately fix two critical security flaws in a widely used programming language amid reports of widespread attempts by hackers to exploit the vulnerabilities.The flaws in PHP, which powers many websites and online services, could allow attackers to take control of web servers, steal data or disrupt services without needing login credentials, Singapore’s Commissioner of Cybersecurity Gwenda Fong said on Thursday.“The threat is immediate,” Fong, who is also CEO of the Singapore" class="entity-link entity-organization" data-entity-id="221281" data-entity-type="organization">Cyber Security Agency of Singapore (CSA), said in a social media post.Working exploits have already been demonstrated and security patches were released on Wednesday, she added.The vulnerabilities, collectively known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619), affect all versions of PHP, according to a CSA security alert issued on Wednesday.The agency said there had been reports of widespread exploitation attempts, as well as the development of multiple proof-of-concept exploits.Cloud services firm Cloudflare recorded millions of attempts to exploit the vulnerabilities following their public disclosure, its CEO Matthew Prince said in a social media post late on Wednesday.
SRCSouth China Morning Post
LANGEN
OutletPrivately owned · Hong Kong SAR China
WORDS172
ENT9
THU · 2026-10-22 · 13:58 GMTBRIEF NSR-2026-1022-121060
NSR-2026-1022-121060News Report·EN·Technology
Singapore pushes for quick action on PHP security flaws as hackers prowl
Singapore's Commissioner of Cybersecurity, Gwenda Fong, has urged organizations to immediately address two critical security flaws in the PHP programming language. These vulnerabilities, known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619), affect all PHP versions and could allow hackers to gain server control, steal data, or disrupt services without credentials.
CNASouth China Morning PostFiled 2026-10-22 · 13:58 GMTOutlet · Privately owned · Hong Kong SAR ChinaRead · 1 min
South China Morning PostFIG 01
Reading time
1min
Word count
172words
Sources cited
3cited
Entities identified
9entities
Quality score
100%
NEWSAR · AI
Singapore's Commissioner of Cybersecurity, Gwenda Fong, has urged organizations to immediately address two critical security flaws in the PHP programming language. These vulnerabilities, known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619), affect all PHP versions and could allow hackers to gain server control, steal data, or disrupt services without credentials. Fong emphasized the immediate threat, noting that working exploits have been demonstrated and security patches were released on Wednesday. The Cyber Security Agency of Singapore (CSA) issued an alert on Wednesday, reporting widespread exploitation attempts and the development of proof-of-concept exploits. Cloudflare also reported millions of exploitation attempts following the public disclosure of these vulnerabilities.
Confidence 0.90Sources 3Claims 5Entities 9
Framing
Technology
National Security
Tone
Mixed Tone
AI-assessed
CalmNeutralAlarmist
Factuality
0.90 / 1.00
Factual
LowHigh
Sources cited
3
Well sourced
FewMany
01
Cloudflare recorded millions of attempts to exploit the vulnerabilities following their public disclosure.
factualCloudflare CEO Matthew Prince
Confidence
1.00
02
The vulnerabilities, collectively known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619), affect all versions of PHP.
factualCSA security alert
Confidence
1.00
03
Working exploits have already been demonstrated and security patches were released on Wednesday.
factualSingapore's Commissioner of Cybersecurity Gwenda Fong
Confidence
1.00
04
The flaws could allow attackers to take control of web servers, steal data or disrupt services without login credentials.
factualSingapore's Commissioner of Cybersecurity Gwenda Fong
Confidence
1.00
05
Organisations in Singapore urged to immediately fix two critical security flaws in PHP.
factualSingapore's Commissioner of Cybersecurity Gwenda Fong
Confidence
1.00
§ 04
Full report
1 min read · 172 wordsKey playerOppositionContextPositiveNeutralNegative
Locations1
php security flaws
1.00
cybersecurity
0.90
hackers
0.80
vulnerabilities
0.80
exploit attempts
0.70
web servers
0.60
cyber security agency of singapore
0.50
data theft
0.50
php2shell
0.40
security patches
0.40
§ 07
Topic connections
Interactive graph Network visualization showing 51 related topics
View Full Graph Person Organization Location Event|Click node to navigate|Edge numbers = shared articles